Is RDP safe? It is one of the most common questions people ask before enabling Remote Desktop on a Windows machine — and the honest answer is: RDP itself is reasonably secure when configured correctly, but it becomes a major risk when exposed carelessly to the internet. The protocol includes strong encryption, but its default port is one of the most scanned and attacked services on the entire internet. This guide explains the real risks in plain language and gives you a practical checklist of best practices that keep your remote sessions safe.
Table of Contents
How RDP Security Works by Default
Modern versions of Remote Desktop Protocol encrypt the session and support Network Level Authentication (NLA), which verifies your credentials before a full desktop session is even established. When both the client and host are up to date and NLA is enabled, an ordinary RDP session is well protected against eavesdropping.
The problem is not usually the encryption — it is the exposure. Every minute, automated bots scan the internet for machines listening on TCP port 3389 (RDP’s default port) and hammer them with stolen or guessed passwords. A weak password on an internet-exposed RDP service is not a theoretical risk; it is one of the most common ways attackers gain their first foothold into a network.
The Main Security Risks of RDP
1. Brute-Force and Password-Spraying Attacks
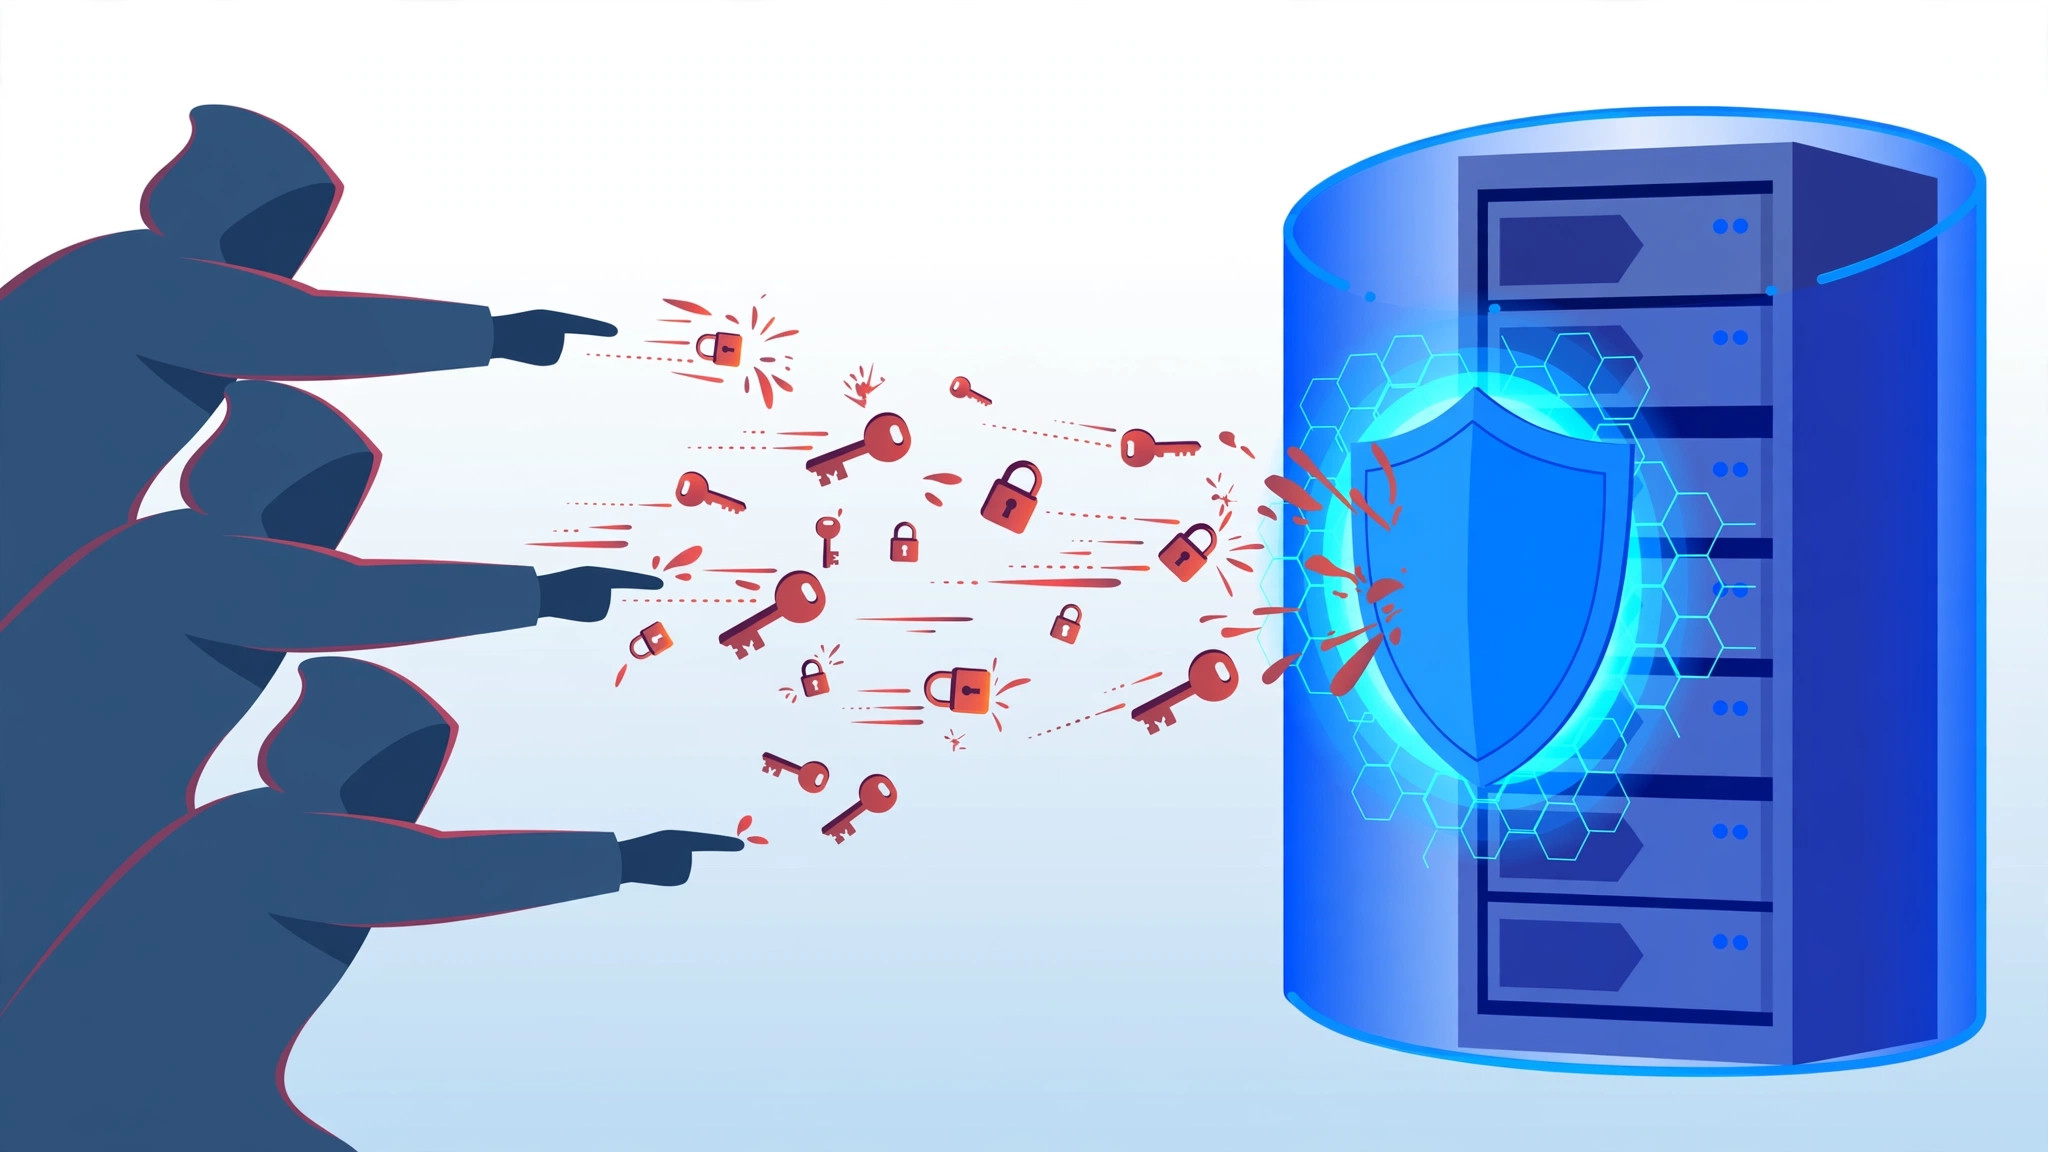
Attackers run automated tools that try thousands of username and password combinations against any RDP server they find. Default or weak credentials — especially on accounts named “Administrator” — fall quickly. This is by far the most common RDP attack in the wild.
2. Unpatched Vulnerabilities
Like all complex software, RDP has had serious bugs. The most famous is BlueKeep (CVE-2019-0708), a “wormable” flaw in older Windows versions that could let an attacker take over a machine without any credentials at all. Microsoft patched it promptly — but machines that skipped updates stayed vulnerable for years. The lesson: unpatched RDP is dangerous RDP.
3. Man-in-the-Middle Attacks on Untrusted Networks
If you connect to RDP over an untrusted network (such as public Wi-Fi) without proper certificate validation, an attacker on the same network could theoretically intercept the connection. Pay attention to certificate warnings instead of clicking through them.
4. Ransomware Entry Point
Security firms consistently report that exposed RDP is among the top initial access vectors for ransomware. Attackers brute-force their way in, then move laterally through the network. For businesses especially, an exposed RDP port is an invitation.
5. Session Hijacking and Credential Theft
If the host machine itself is compromised by malware, saved RDP credentials and active sessions can be stolen. This is a risk of the endpoint, not the protocol — but it is worth remembering that RDP security depends on both ends being clean.
RDP Best Practices: The Essential Checklist
Never Expose Port 3389 Directly to the Internet
This is the single most impactful step. If you need remote access over the internet, connect through a VPN into your network first, then use RDP inside the VPN tunnel. Alternatives include Remote Desktop Gateway, which tunnels RDP over HTTPS, or a reputable remote-access service with built-in encryption. An RDP port sitting open on the public internet will be found and attacked — usually within hours.
Use Strong, Unique Passwords (and Fewer Admin Accounts)
Every account allowed to connect via RDP needs a long, unique password — ideally generated by a password manager. Consider renaming or disabling the default “Administrator” account, since attackers always try it first. Better still, create a dedicated standard user account for remote access instead of connecting as a full administrator.
Keep Network Level Authentication Enabled
NLA forces authentication before the session starts, which blocks a whole class of attacks against the login screen itself. It is enabled by default on modern Windows — leave it that way. You can verify it under sysdm.cpl > Remote tab: the option “Allow connections only from computers running Remote Desktop with Network Level Authentication” should be checked.
Install Windows Updates Promptly
Critical RDP vulnerabilities are fixed through Windows Update. Enable automatic updates on any machine that accepts RDP connections, and reboot when updates require it. A fully patched system closes the door on known exploits like BlueKeep.
Restrict Who Can Connect
Open sysdm.cpl > Remote tab > Select Users and review the list regularly. Remove accounts that no longer need access. If your firewall supports it, restrict inbound RDP traffic to specific IP addresses (your office IP, your VPN range) rather than allowing the whole internet.
Enable Account Lockout Policies
Account lockout stops brute-force attacks cold: after a set number of failed logins, the account locks temporarily. Configure it via Local Security Policy (secpol.msc) > Account Policies > Account Lockout Policy — for example, lock out after 5 failed attempts for 30 minutes. This single setting defeats most automated password guessing.
Turn Off RDP When You Do Not Need It
An unused service cannot be attacked. If you only need remote access occasionally, disable Remote Desktop in Settings > System > Remote Desktop when you are done. It takes ten seconds to re-enable later.
Watch for Certificate Warnings
When connecting, if the client warns that the remote computer’s identity cannot be verified, stop and investigate before proceeding — especially on unfamiliar networks. On a trusted home network with a self-signed certificate this warning is normal, but on public Wi-Fi it deserves scrutiny.
Consider Changing the Default Port (Minor Benefit)
You can change RDP’s listening port in the registry at HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp (the PortNumber value), plus a matching firewall rule. Be honest with yourself about what this achieves: it evades only the laziest port scans. Treat it as a small extra layer, never as a substitute for the measures above.
Is RDP Safe for Business Use?
Yes — countless organizations use RDP daily as part of a properly designed remote-access strategy. The difference between safe and unsafe business RDP is architecture: VPN or RD Gateway in front of it, multi-factor authentication where possible, centralized logging of logon events, and prompt patching. If you are administering servers, also consider dedicated privileged-access tooling rather than exposing RDP on every machine.
Conclusion
So, is RDP safe? The protocol’s encryption is solid, and with NLA, strong passwords, prompt updates, and — most importantly — no direct internet exposure, RDP is a perfectly reasonable remote-access tool for home and business use. The danger comes from the default configuration left facing the public internet with a weak password. Follow the checklist above, and you remove the attack paths that account for nearly all real-world RDP compromises.
Frequently Asked Questions
Is it safe to leave Remote Desktop enabled all the time?
On a trusted private network with strong passwords and updates installed, yes. If the machine is reachable from the internet, it is much safer to enable RDP only when needed, or to require a VPN connection first.
Has RDP ever been hacked?
Yes — vulnerabilities like BlueKeep allowed remote takeover of unpatched systems, and brute-force attacks against weak passwords succeed every day. Every major incident, however, involved missing patches, weak credentials, or direct internet exposure — all preventable with the practices in this guide.
Is RDP encrypted?
Yes. Modern RDP sessions are encrypted, and Network Level Authentication adds credential verification before the session begins. The encryption protects against eavesdropping; it does not protect against someone guessing your password, which is why strong credentials matter.
What is safer than exposing RDP to the internet?
A VPN connection into your network (then RDP inside the tunnel), Remote Desktop Gateway (RDP over HTTPS), or a managed remote-access solution with built-in encryption and multi-factor authentication. All three keep port 3389 closed to the public internet.